Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

Explore practical insights into cybersecurity risk, from identifying threats and vulnerabilities to understanding their potential business impact. Learn how effective risk management helps organizations protect critical assets, reduce exposure, strengthen resilience, and make smarter security decisions.

Subcategories from this category:

Threat Advisory

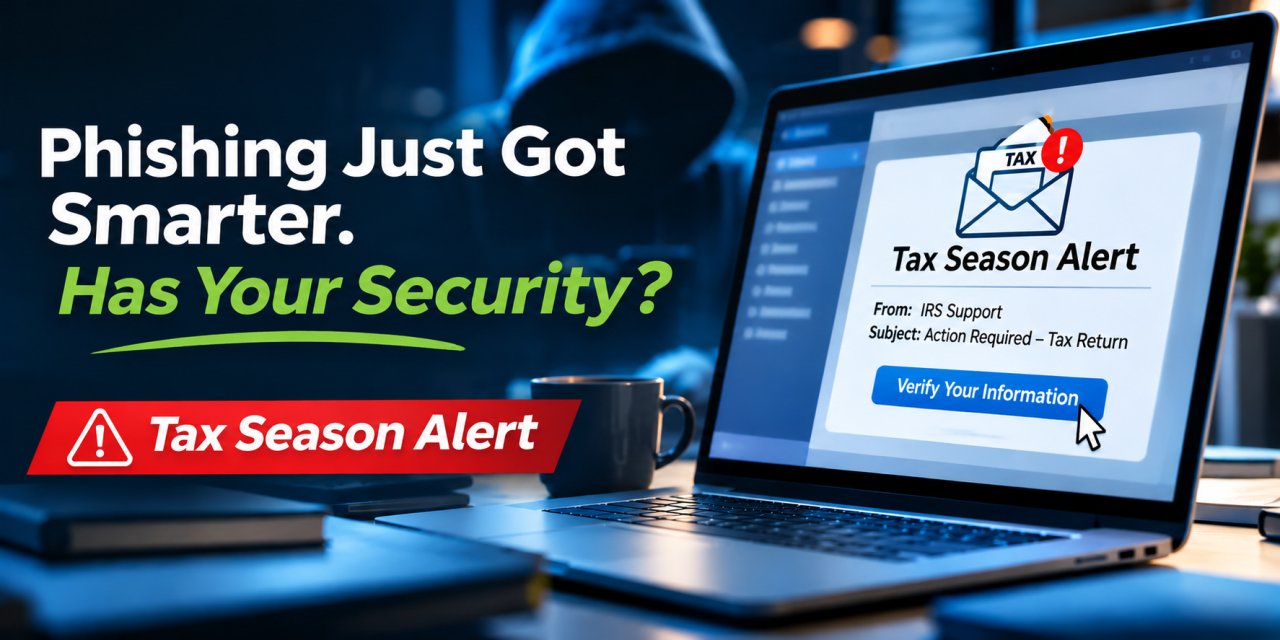
The Payment That Never Arrived: Tax Season, AI Phishing, and the MFA Decision That Cost

Tax-Season-Phishing-Alert
Every year, the weeks between January and April turn inboxes into a minefield. W-2s go out. Accountants request documents. Payroll providers send notices. Vendors chase invoices before the books close. It's the busiest, most paperwork-heavy stretch of the year, and cybercriminals plan for it just like your finance team does.
Continue reading
  209 Hits

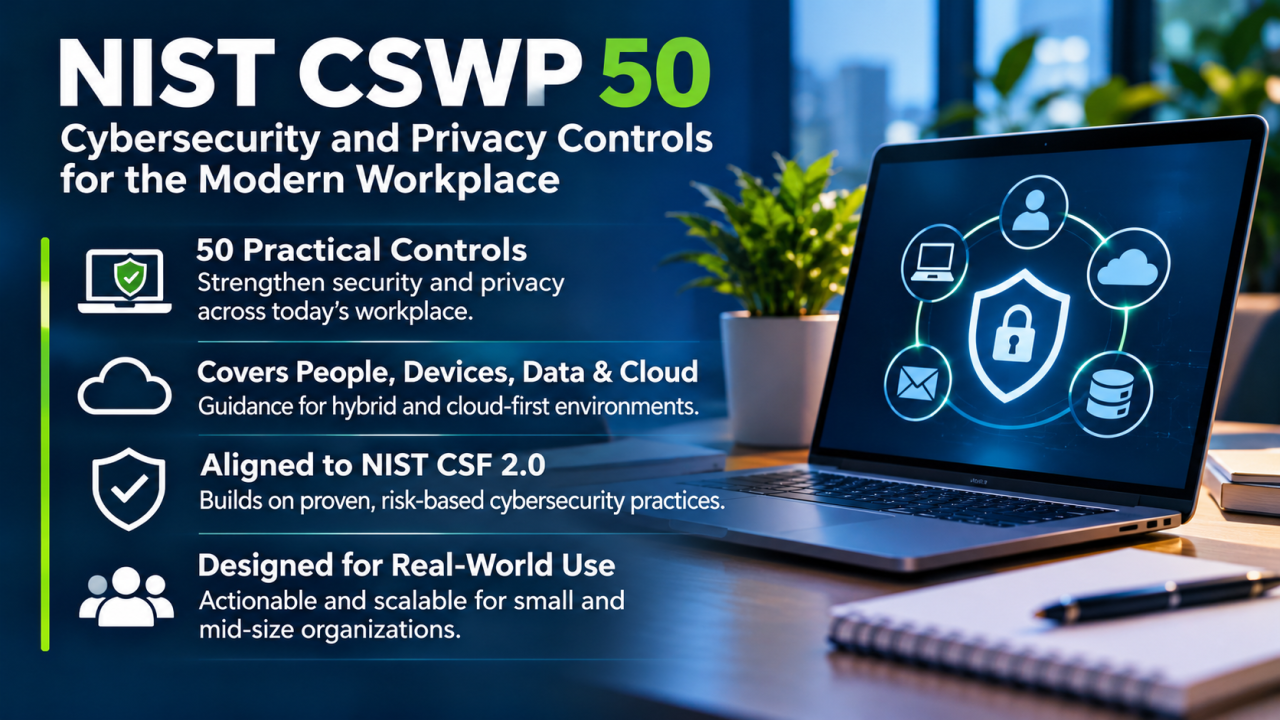
NIST’s New Small Business Guide Lands the Same Week a Live VPN Threat Proves Why It Matters

NIST-CSWP-50_-Modern-Workplace-Securit_20261111-000020_1

This week, NIST published its first cybersecurity guide written specifically for businesses too small to have an IT department and days later, CISA confirmed active exploitation of a VPN flaw sitting on firewalls many of those same businesses rely on, proving the guidance couldn't have arrived at a better time.

Continue reading
  311 Hits

Cybersecurity Threat Advisory: Exploited Cisco Firewall Flaw Can Knock Your VPN Offline

LBT-Threat-Advisory-Banner

Threat update

Cisco has confirmed that attackers are actively exploiting a high-severity flaw in Cisco Secure Firewall ASA and Firepower Threat Defense (FTD). Tracked as CVE-2026-76418 (CVSS 8.6), the bug lets anyone on the internet send a crafted request to your VPN login page and force the firewall to reboot. No username or password needed. Keep sending those requests and the firewall keeps going down, taking your remote workers, branch connections, and anything else behind it along for the ride. CISA added this one to its Known Exploited Vulnerabilities catalog on October 29. If you run Cisco firewalls with SSL VPN, it belongs at the top of this week's patch list.

Continue reading
  547 Hits

When a Hospital Goes Dark: What the UNM Health Ransomware Attack Teaches Every SMB About Cyber Risk and Compliance

Red-Alert-in-the-Server-Roo_20261103-032438_1

When a single ransomware attack can cancel surgeries, divert ambulances, and cancel classes within hours, "we're too small to be a target" stops being a credible security strategy for any organization including yours.

Continue reading
  801 Hits

Your Meetings Are Becoming Business Intelligence. But Who Controls What AI Remembers?

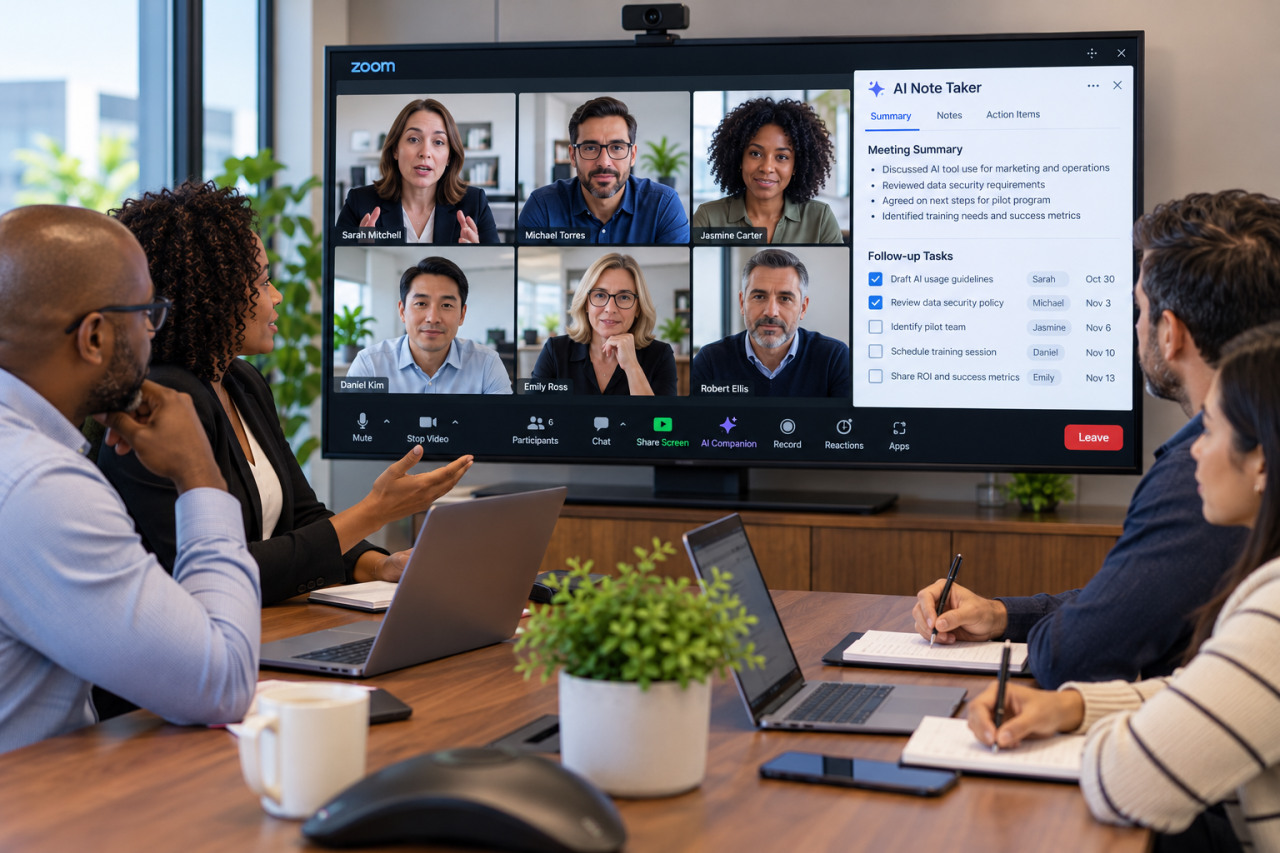
CollaborativeAIPoweredZoomMeeting
New AI tools can turn everyday conversations into searchable knowledge and follow-up tasks. For small businesses, the opportunity is real and so is the responsibility to protect the information behind it.
Continue reading
  586 Hits

Your Backups Are the Target Now: What This Week's SafePay Ransomware Advisory Means for Your Business

data-backup
Federal agencies just confirmed that one of 2026's most active ransomware gangs doesn't just encrypt your data it hunts down and deletes your backups first, which means "we have backups" is no longer a safety net unless those backups are built to survive the attack itself.
Continue reading
  588 Hits

Your MFA Didn't Fail You, Your Session Did: Inside the 79-Company Microsoft 365 Breach

hero_image

Employees did everything security training told them to do typed the password, approved the MFA prompt, and attackers walked into their inbox anyway, because this attack never needed to beat MFA at all; it just stole the session that came after it.

Continue reading
  584 Hits

Cybersecurity Threat Advisory: Fake PuTTY Downloads Are Hunting Your IT Admins

Threat-Advisory-Banner3

Threat update

Attackers are using poisoned Google search results and sponsored ads to steer IT administrators to fake PuTTY download sites. The installer looks right, and PuTTY even opens and works like normal. Meanwhile, malware is quietly installing itself in the background, stealing browser sessions and credentials, and watching the admin's screen. No software flaw is involved. The attack only needs one busy admin to click the first search result. If your team ever grabs tools from a quick Google search, now is the time to put a stop to it. 

Continue reading
  729 Hits

When “Fully Patched” Isn’t Enough

CybersecurityUpdateDashboard
In a single week, Microsoft shipped a record-shattering 1,400+ patches, attackers breached a VPN appliance that was already fully up to date, and CISA added nine actively exploited flaws to its must-patch list a stark reminder that for small and mid-sized businesses, "we installed the updates" is no longer the same thing as "we're secure."
Continue reading
  711 Hits

ConnectWise Cloud Backup (Formerly SkyKick) Incident: What MSP Clients Should Check Today

img-connectwise-hero
We've spent years telling clients that backups are the safety net. If everything else goes wrong, you can get your data back. So, it stings a bit to write a post about a backup platform possibly being the way an attacker got into Microsoft 365.
Continue reading
  1106 Hits

Cybersecurity Threat Advisory: Critical SonicWall SMA 1000 Flaws Open Remote Access Gateways to Attack

Threat-Advisory-Banner3

Threat update

SonicWall has released fixes for four vulnerabilities in its SMA 1000 Secure Mobile Access appliances, the gateways many organizations use to give staff remote access to internal systems. The worst of the four scores a perfect 10.0 and can be exploited by an attacker with no username or password. SonicWall hasn't reported active exploitation yet, but security teams are already seeing increased scanning of internet-facing SMA 1000 devices. If you run one, patch it now.

Continue reading
  808 Hits

Cybersecurity Threat Advisory: Milk Dragon Phishing Kit Uses Fake Social Media Deals to Steal Cards and One-Time Passcodes

Threat-Advisory-Banner3

Threat update

A phishing kit called Milk Dragon (also known as NaiLong) is being sold to criminals as a subscription service, and it is built for one job: turning a "too good to be true" social media deal into a fraudulent card charge. Victims click a discount ad on Facebook or TikTok, land on a cloned store that looks like a brand they trust and enter their card details. The kit then grabs the one-time passcode their bank sends and uses it on the spot. Your business is exposed in two ways. Employees may shop on these sites with company cards, and your own brand could be the one being copied.

Continue reading
  880 Hits

Your Team's "Vibe Coded" App Might Already Be Leaking Customer Data

Holographic-Shield-Over-Server-Rack_20261008-101250_1

A single security scan this week found over 16,000 publicly exposed databases built with AI coding tools — a wake-up call that the rush to build fast with AI is quietly creating a breach crisis for businesses of every size, not just tech giants.

Continue reading
  1169 Hits

Remote Access Is This Week's Battleground: Here's What Your Business Needs to Know

remoge_access_featured_image
Two fresh warnings, a SANS-flagged wave of attacks abusing legitimate remote-support software and a newly exploited Citrix NetScaler zero-day with a federal patch deadline this week, both target the exact remote-access tools SMBs and their IT providers rely on every day.
Continue reading
  960 Hits

Cybersecurity Threat Advisory: TrustSink Turns Microsoft Entra ID's MFA Against You to Steal Passwords

Threat-Advisory-Banner3

Threat update

Researchers have demonstrated a new attack technique called TrustSink that abuses the multi-factor authentication (MFA) features in Microsoft Entra ID, the identity service behind Microsoft 365. An attacker who gains control of a high-level admin account can quietly add a fake MFA provider to the tenant. From then on, every time a user signs in, that fake provider captures their password in plain text while the login completes normally. Organizations that use Microsoft 365 should review their Entra ID authentication settings and lock down admin accounts now.

Continue reading
  969 Hits

Critical Cisco SD-WAN Flaw Under Active Attack: What Business Owners Need to Do Now

img-cisco-sdwan
Cisco has confirmed that attackers are actively exploiting a critical vulnerability in the software many businesses use to connect their offices together. The flaw, tracked as CVE-2026-76504 and rated 9.8 out of 10 on the CVSS severity scale, affects Cisco Catalyst SD-WAN Manager. It lets a remote attacker slip past a login check and gain administrator-level access to a protected management API. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has already added it to its Known Exploited Vulnerabilities (KEV) catalog and gave federal agencies until October 3, 2026 to fix it.
Continue reading
  1000 Hits

Zimbra Email Servers Hacked Before the Flaw Was Even Announced: What You Need to Know

img-zimbra
A fix for a critical Zimbra email server flaw was available for more than three weeks before the public was told about it, and attackers used that time. Microsoft Threat Intelligence reports that threat actors exploited CVE-2026-73570 (CVSS 8.9), an unauthenticated operating system command injection vulnerability in the Zimbra Collaboration Suite, for weeks before it was disclosed. The Shadowserver Foundation counted 274 compromised Zimbra servers in a single recent week.
Continue reading
  840 Hits

Critical Citrix NetScaler Zero-Days Are Under Active Attack: What Your Business Needs to Do This Week

server-room-closeup-critical-error

A pair of critical, unauthenticated zero-day vulnerabilities in Citrix NetScaler are being actively exploited right now and with roughly 23,000 internet-exposed devices worldwide, this is a "patch today, not next sprint" moment that shows exactly why continuous vulnerability management can't be a once-a-quarter checkbox for any growing business.

Continue reading
  910 Hits

Cybersecurity Threat Advisory: WordPress "Click2Shell" Flaw Turns One Admin Click into Full Site Takeover

Threat-Advisory-Banner3

Threat update

A newly disclosed vulnerability in WordPress Core, nicknamed Click2Shell, allows an attacker to take control of a WordPress website if a logged-in administrator simply opens a specially crafted link. No further clicks, prompts, or approvals are needed. WordPress fixed the issue in version 7.1.1 and backported the fix to every supported branch back to 4.7. Because proof-of-concept code is now public, any organization running WordPress should confirm its sites are updated today.

Continue reading
  792 Hits

An AI Agent Hacked a Security Nonprofit Through Its Helpdesk: Lessons from the DIVD Breach

img-zammad
A cybersecurity nonprofit whose entire mission is warning others about vulnerabilities has itself been breached, and it believes an AI agent did the hacking. On September 24, 2026, the Dutch Institute for Vulnerability Disclosure (DIVD) announced that attackers had broken into its systems. Over the following week, DIVD revealed that the attacker exploited two previously unknown vulnerabilities in Zammad, a popular open-source helpdesk and ticketing system, and stole volunteer data. Zammad has not yet released official patches.
Continue reading
  855 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024